SELF-HOSTED WORKSHOP
I build apps, security tools, games, or anything that feels like it could be fun or help me.
Everything here runs on my personal homelab.
Self-hosted on my own homelab.
Secured by design
Development
What I build
Games, apps and security tools, the things I like building.
- > Unity & web games
- > Full-stack apps
- > Security PoCs & writeups
- > Low-level / assembly
Infrastructure & self-hosting
How it runs
The homelab that runs everything here, including this site.
- > Proxmox virtualization
- > OPNsense firewall & routing
- > Reverse proxy + TLS
- > Docker-hosted services, this site included
Projects
Selected work
All projects →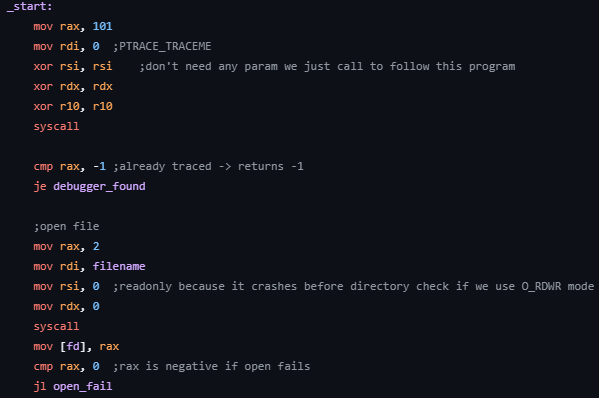
ELF Infector
2025experimentalWriteup-only
A proof-of-concept ELF infector: it rewrites a binary's PT_NOTE segment into a PT_LOAD segment to run custom x86-64 shellcode, a study of ELF internals and code injection.
- cyber
- low-level
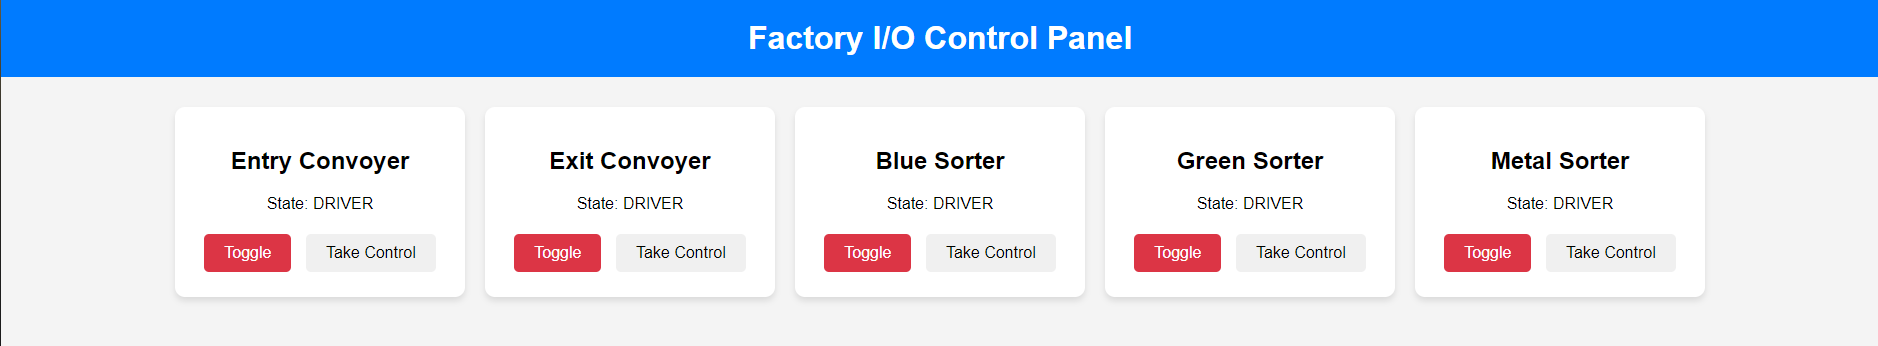
SCADA Flask / FactoryIO
2025experimentalWriteup-only
A short study of SCADA security flaws: a Flask interface takes manual Modbus control of coils in a FactoryIO sorting line, showing how an operator UI can override the process, and how to secure it.
- cyber
- industrial
HOSTED AT HOME
How it's hosted
Everything on this page is served from my own hardware at home, no cloud host, no third-party platform. Here's the stack that keeps it running.
Proxmox
The hypervisor everything runs on, each service lives in its own isolated VM or container.
OPNsense
Firewall and router at the edge, segments the network and controls what's allowed in from outside.
Reverse proxy
Sits in front of every service, terminates TLS and routes each hostname to the right container, this site included.
Docker
Services ship as containers with docker-compose, so any of them can be rebuilt and redeployed from source.
TLS
HTTPS everywhere, with certificates issued and renewed automatically.